

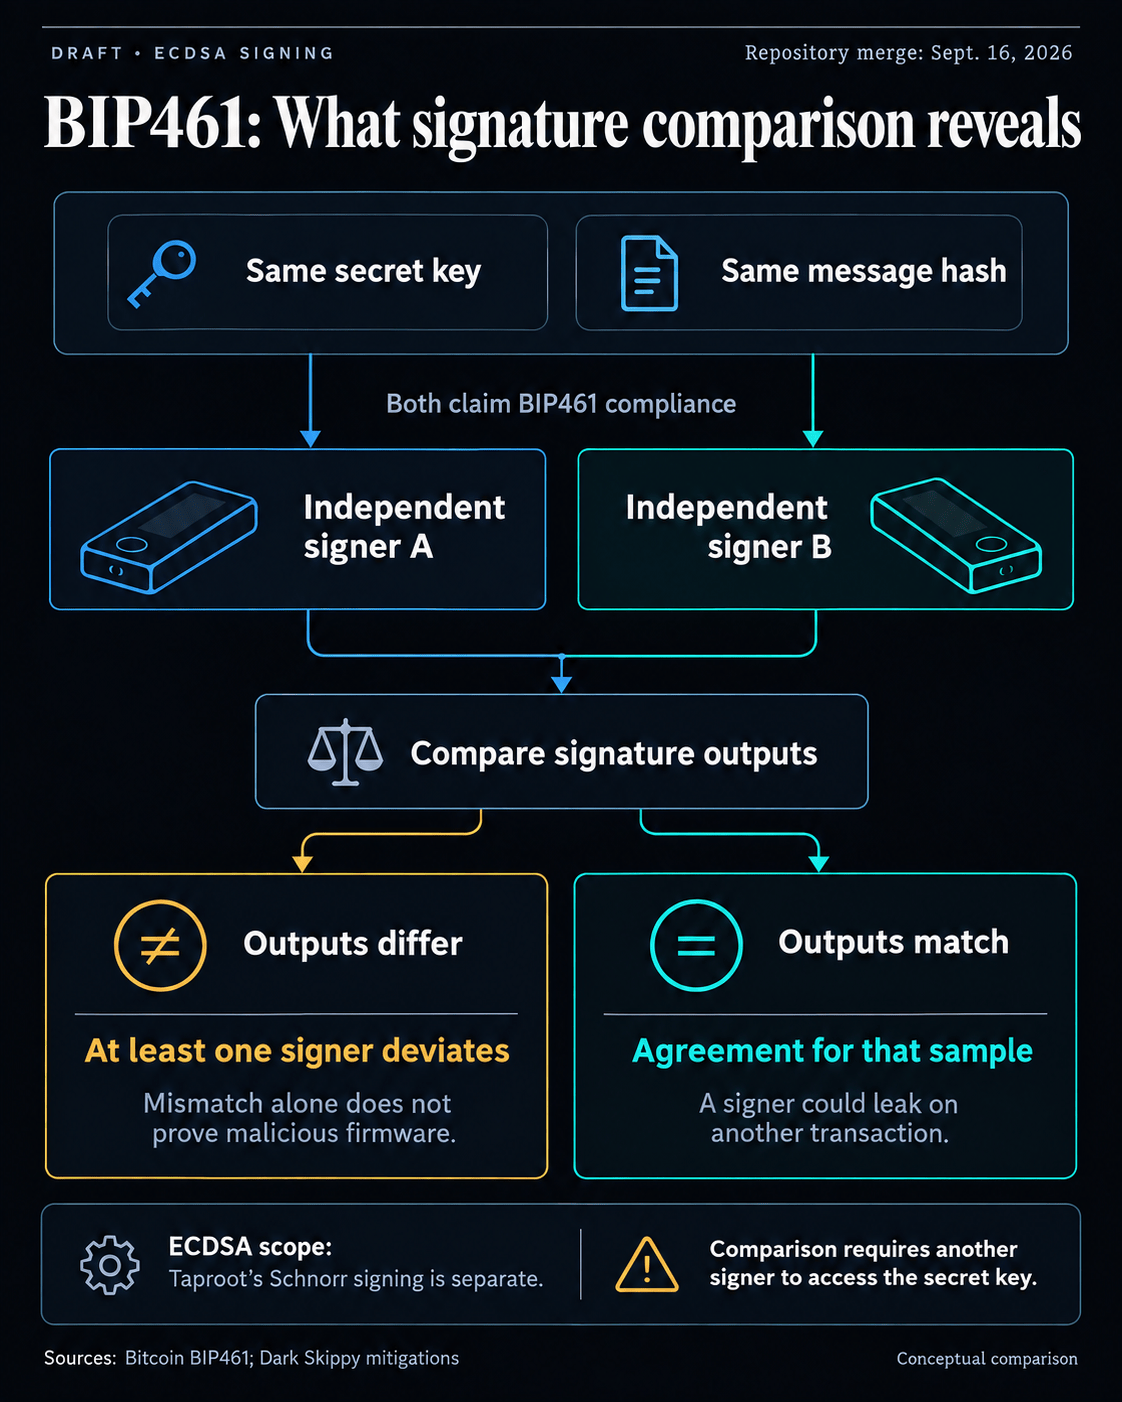
Bitcoin improvement proposal BIP461 could make a hidden route for leaking wallet secrets easier to detect. The draft defines a common signing procedure for ECDSA, an existing Bitcoin signature scheme.
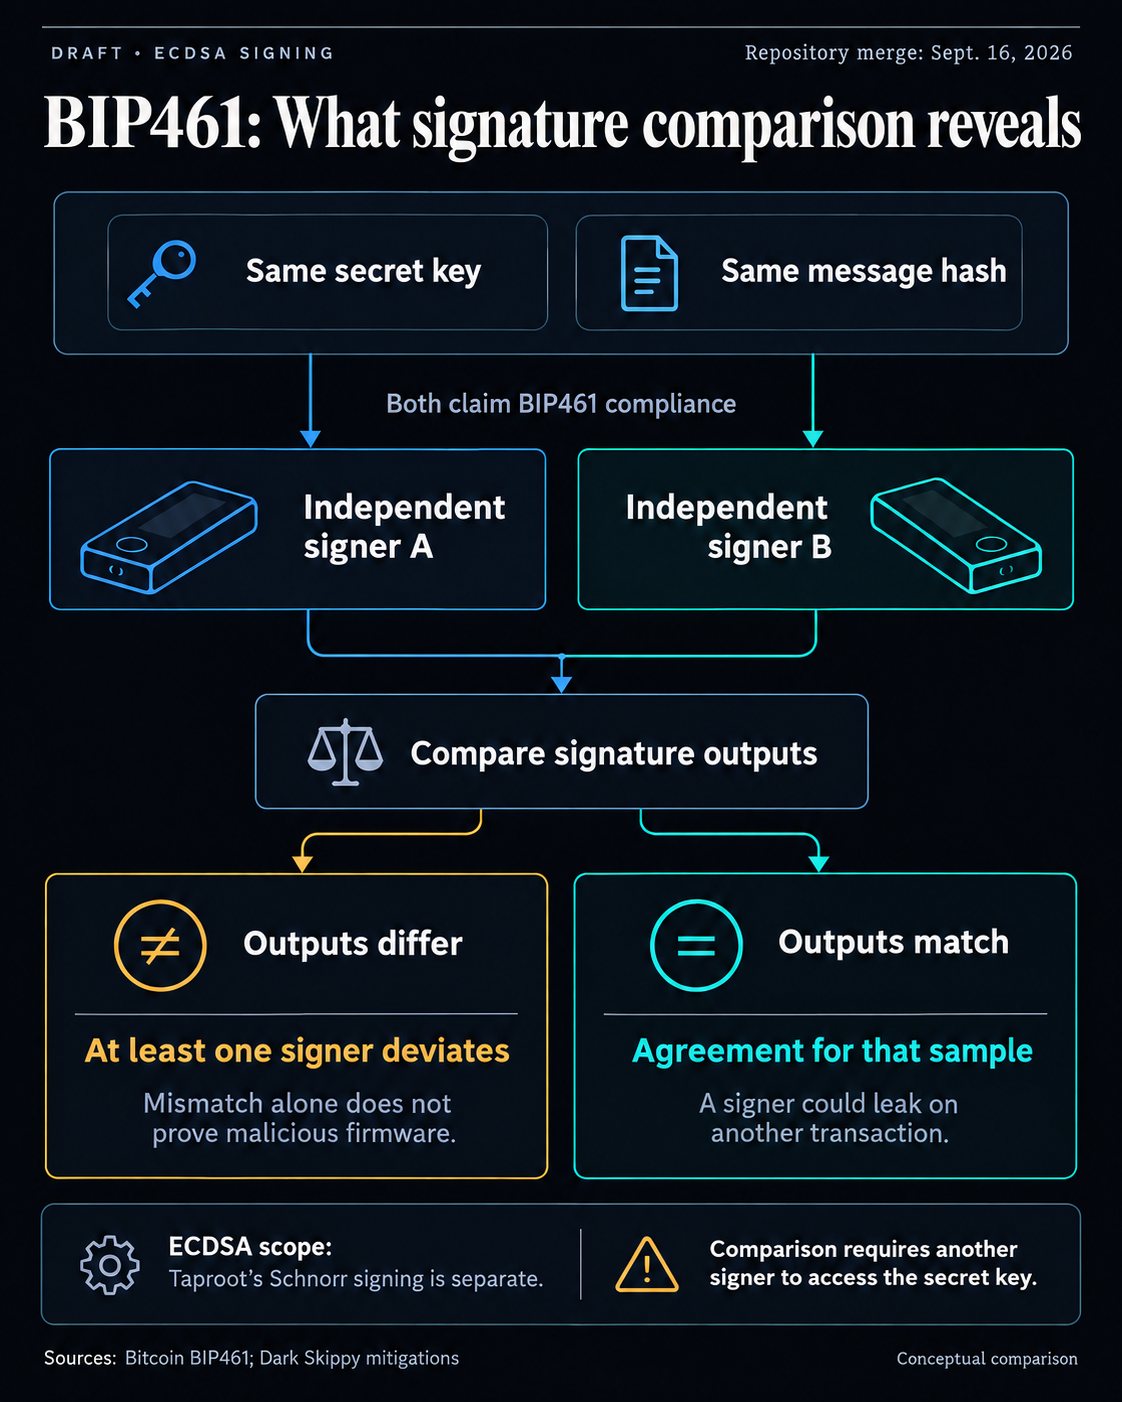
Independent compliant signers should produce identical signatures for the same secret key and message hash, creating a benchmark for detecting departures that could conceal key leakage.
Authored by Liam Gilligan, the proposal was merged into the BIPs repository on Sept. 16 and remains marked Draft. Its signatures work under existing Bitcoin consensus rules, so implementing this signing procedure requires no consensus change.
Comparing signatures for deviations
ECDSA allows a signer choices while creating a valid signature, including the nonce, a temporary value used in signing. Malicious firmware can exploit that freedom to hide key material in signatures that still pass verification, and BIP461 fixes those choices through a specified deterministic procedure.
Bitcoin’s acceptance of a signature cannot establish that its creation kept the key safe. A common specification supplies an expected output against which the signer’s behavior can be checked.
The comparison requires identical inputs and the exact same standard, including access to the secret key on another independent signer. That extra exposure is a practical cost of reproducing the signature. Different results for the same key and message hash show that at least one signer is not following BIP461.
An honest implementation using another valid ECDSA procedure can also disagree. A mismatch warrants investigation into compliance, but its cause remains unresolved. The comparison alone cannot identify a malicious device or demonstrate theft.
The prescribed algorithm also keeps signatures to at most 70 bytes in the standard DER encoding, excluding Bitcoin’s one-byte sighash flag.
The Dark Skippy disclosure pointed out that corrupted firmware can embed seed material in transaction signatures. In their original disclosure, the researchers said they had not seen the technique in the wild.
Dark Skippy’s original demonstration uses Schnorr signing, while BIP461 specifies ECDSA. Taproot uses the separate BIP340 Schnorr scheme, so this draft does not directly standardize a remedy for that demonstration.
The researchers’ mitigation discussion warned that a malicious signer could leak only on a selected transaction, so a device could produce compliant signatures in a test and leak on another transaction.
At the September merge, a reviewer said test vectors and a reference implementation were needed for BIP461 to advance to Complete.
For wallet users, its potential value is a shared benchmark that could make deviations visible. Delivering that value still depends on compliant implementations and comparisons that account for both detection limits and the risks of handling secrets.
The post New Bitcoin upgrade catches hidden key leaks hiding the exact fix appeared first on KryptoNews.